


Personal Data Protection Office Discusses Cyber Resilience in the Science and Higher Education Sector at Conference in Rzeszów
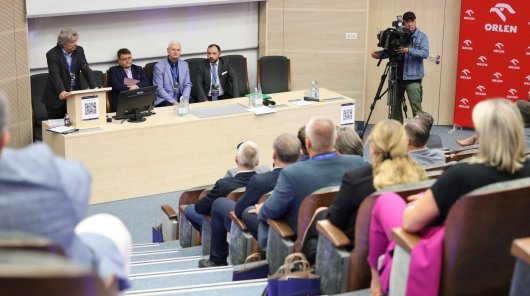
Konrad Komornicki, Deputy President of the Personal Data Protection Office, took part in the conference entitled ‘Information Security Management in the Science and Higher Education Sector and Public Administration: NIS2 Requirements and the Cyber Resilience of Essential and Important Entities’, held on 17 and 18 September 2026 at the University of Rzeszów.
The conference was opened by Konrad Komornicki, Deputy President of the Personal Data Protection Office. The event focused on issues relating to information security management, cyber resilience and NIS2 requirements. Discussions brought together representatives of public administration, academia and business, as well as experts in data protection and cybersecurity.
‘Effective information security management requires a comprehensive approach today. The development of new technologies and the changing regulatory environment mean that personal data protection and cybersecurity are increasingly interconnected. This makes cooperation, the exchange of experience and raising awareness within organisations particularly important. This applies to public administration, academia and business alike,’ said Konrad Komornicki, Deputy President of the Personal Data Protection Office.
One of the main topics on the first day of the conference was the impact of NIS2 on the functioning of universities, public administration and businesses as essential and important entities. The programme covered, among other things, the responsibilities of university authorities and the development of cyber resilience, not only in terms of technology, procedures and regulatory compliance, but also among academic and administrative staff and students.
Andrzej Zieliński, Deputy Director of the Inspections and Breaches Department at the Personal Data Protection Office, took part in a panel entitled ‘GDPR + NIS2 + DORA + AI Act + Integrated Security Management within Organisations’. The discussion covered, among other things, the legal framework for NIS2 and the overlap between regulatory frameworks, the role of the data protection officer in the age of artificial intelligence, and audit requirements.
Andrzej Zieliński emphasised that personal data are now involved in almost every area of an organisation’s activities. Consequently, GDPR requirements should not be treated as a separate element of security management, but should form an integral part of a coherent system that also takes into account the requirements arising from the Act on the National Cybersecurity System, DORA and the AI Act. The Personal Data Protection Office expert also highlighted the practical importance of this approach in crisis management systems. As an example, he cited incident response procedures, which should ensure an interdisciplinary approach. This enables an organisation to fulfil its notification obligations under the various regulatory frameworks efficiently and simultaneously, through a single, coherent process.
The conference also addressed insurance against the consequences of incidents as an element of business continuity management, cyber warfare, disinformation and national security. The programme covered, among other things, phishing and social engineering campaigns, deepfake technology and measures to combat modern fraud involving artificial intelligence.
The second day of the event had a practical focus. Participants discussed cyber threats, incidents and crisis management, as well as the practical implementation of NIS2 requirements in public sector organisations. Workshops were also scheduled on auditing organisational readiness for NIS2 and the National Interoperability Framework (KRI) requirements, applying the AI Act in academia, and organisational business continuity.
The conference was held at the University of Rzeszów as part of the ‘Podkarpackie Security Forum 2026 – Shaping Local Security: Theoretical and Practical Perspectives’.